

[2026] MS-102 Actual Exam Dumps, MS-102 Practice Test
RealExamFree MS-102 dumps & Microsoft 365 Certified sure practice dumps
NEW QUESTION # 296
You have three devices enrolled in Microsoft Endpoint Manager as shown in the following table.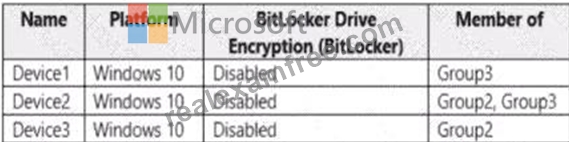
The device compliance policies in Endpoint Manager are configured as shown in the following table.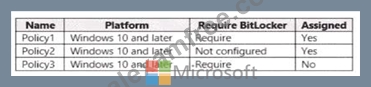
The device compliance policies have the assignments shown in the following table.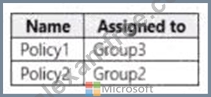
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.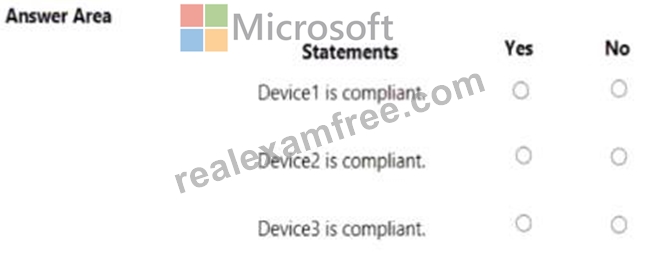
Answer:
Explanation:
Explanation: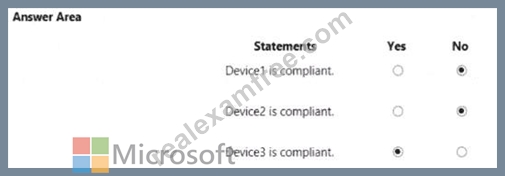
NEW QUESTION # 297
You have a Microsoft 365 E5 subscription that contains a user named User1.
The subscription has a single anti-malware policy as shown in the following exhibit.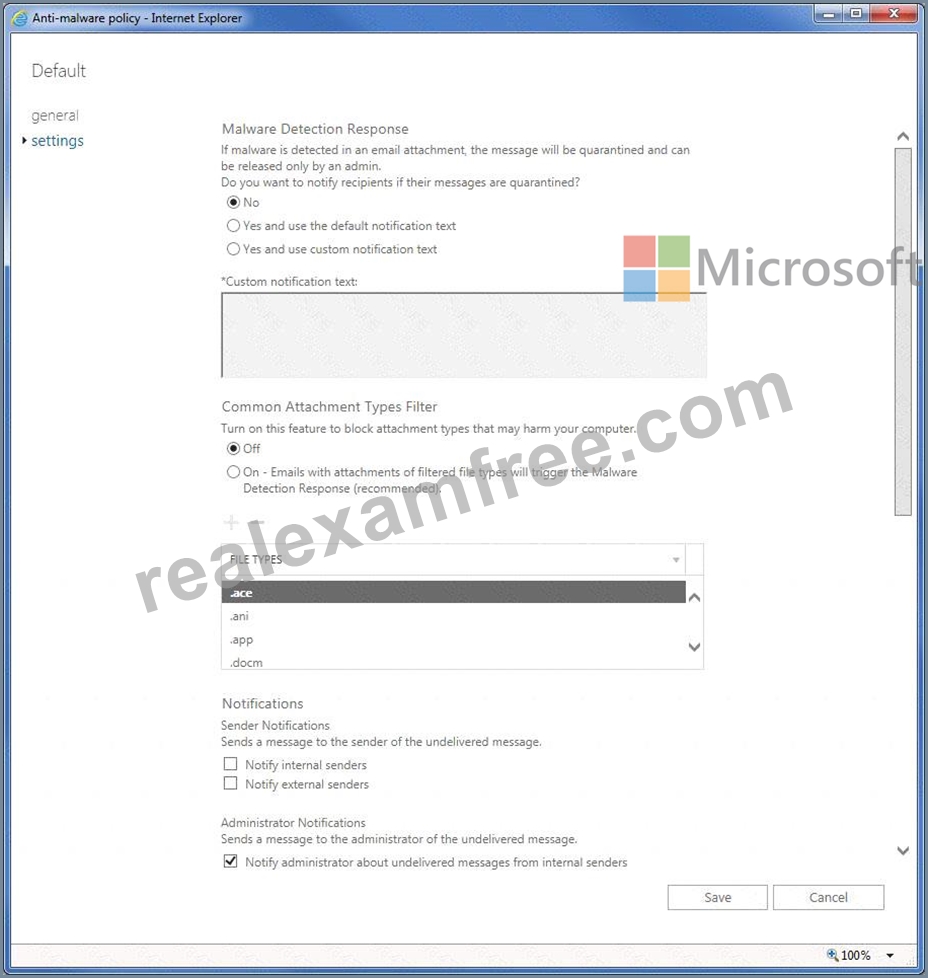
An email message that contains text and two attachments is sent to User1. One attachment is infected with malware.
How will the email message and the attachments be processed?
- A. Both attachments will be removed. The email message will be quarantined, and User1 will receive a copy of the message containing the original text and a new attachment that includes the following text:
'Malware was removed." - B. Both attachments will be removed. The email message will be quarantined, and Used will receive an email message without any attachments and an email message that includes the following text: 'Malware was removed.'
- C. The email message will be quarantined, and the message will remain undelivered.
- D. The malware-infected attachment will be removed. The email message will be quarantined, and User1 will receive a copy of the message containing only the uninfected attachment.
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/security/office-365-security/anti-malware-protection?view=o365
NEW QUESTION # 298
You have a Microsoft 365 E5 subscription.
All corporate Windows 11 devices are managed by using Microsoft Intune and onboarded to Microsoft Defender for Endpoint.
You need to meet the following requirements:
* View an assessment of the device configurations against the Center for Internet Security (CIS) vl.0.0 benchmark.
* Protect a folder named C:\Folder1 from being accessed by untrusted applications on the devices.
What should you do? To answer, select the appropriate options in the answer area.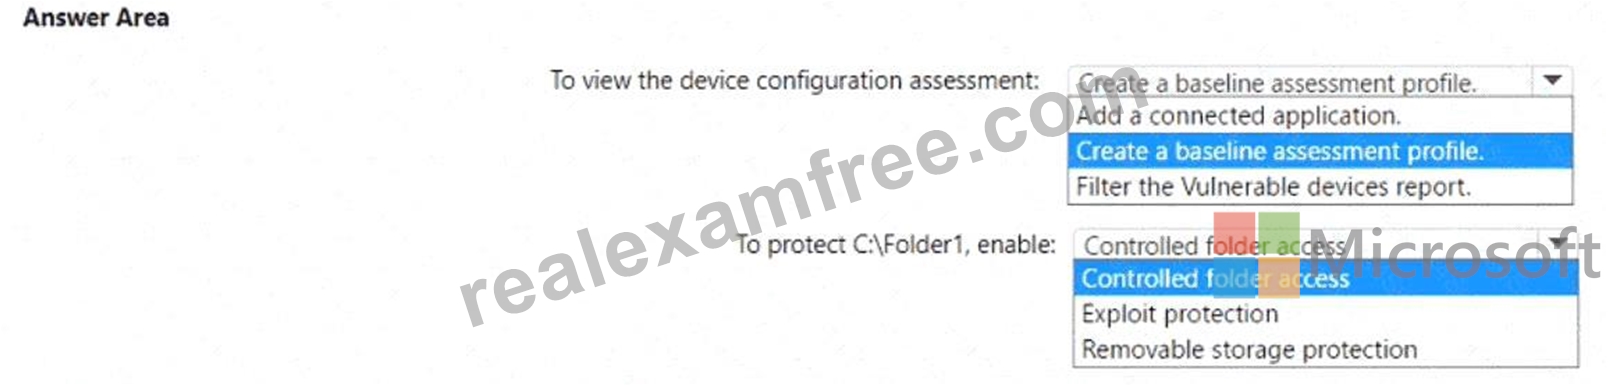
Answer:
Explanation: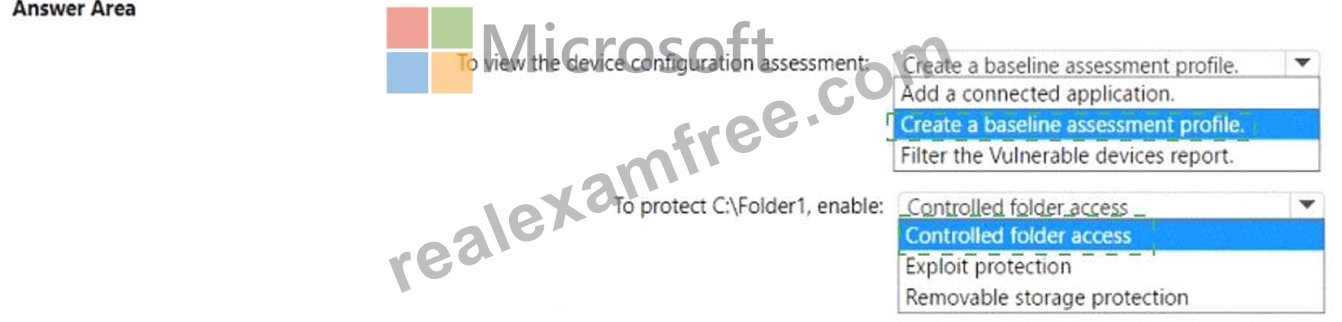
Explanation: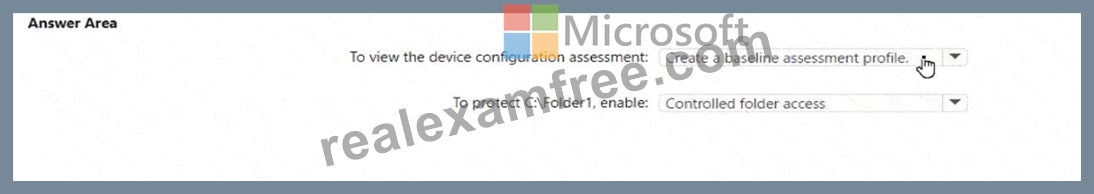
NEW QUESTION # 299
You have a Microsoft 365 E5 subscription that uses Microsoft Intune.
You have devices enrolled in Intune as shown in the following table.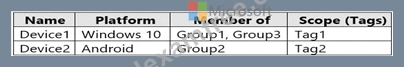
You create the device configuration profiles shown in the following table.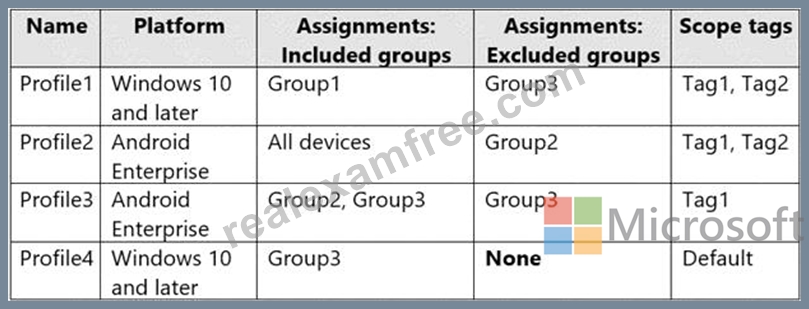
Which profiles will be applied to each device? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.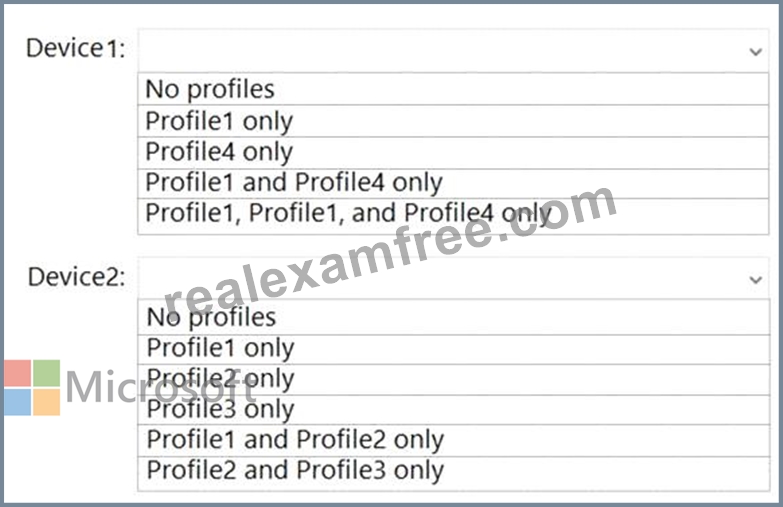
Answer:
Explanation: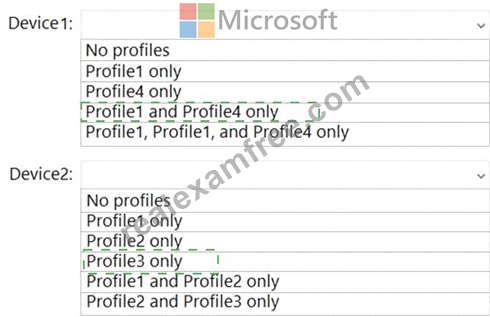
Explanation: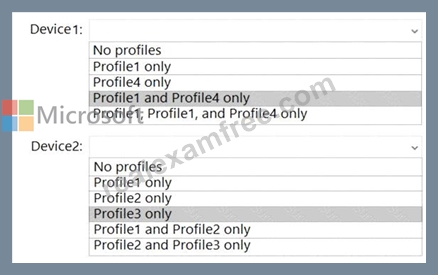
NEW QUESTION # 300
You have a Microsoft 365 E5 subscription.
You need to be alerted when Microsoft 365 Defender detects high-severity incidents.
What should you use?
- A. a custom detection rule
- B. an alert policy
- C. a notification rule
- D. a threat policy
Answer: B
NEW QUESTION # 301
From the Microsoft Purview compliance portal, you create a retention policy named Policy 1.
You need to prevent all users from disabling the policy or reducing the retention period.
How should you configure the Azure PowerShell command? To answer select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.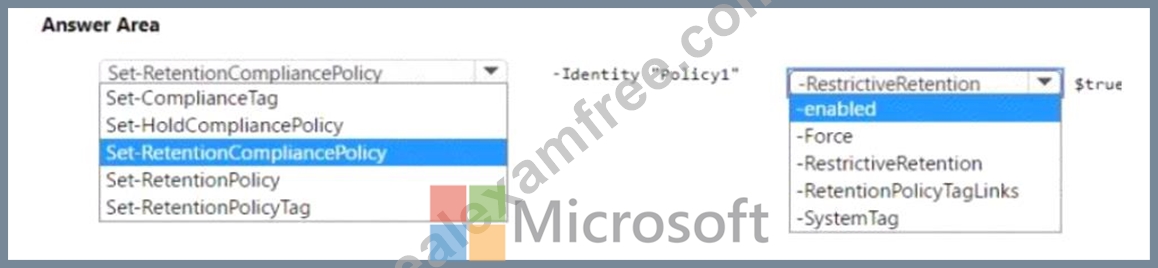
Answer:
Explanation: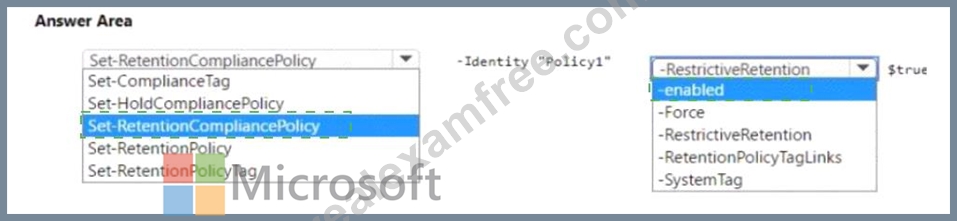
Explanation:
NEW QUESTION # 302
You have a hybrid Azure Active Directory (Azure AD) tenant and a Microsoft Endpoint Configuration Manager deployment.
You have the devices shown in the following table.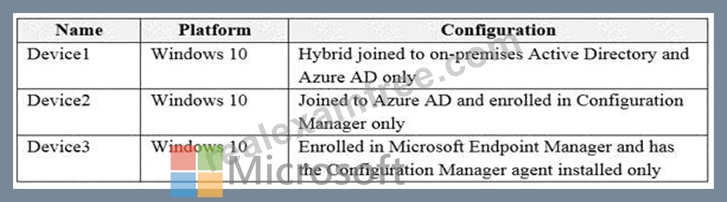
You plan to enable co-management.
You need to identify which devices support co-management without requiring the installation of additional software.
Which devices should you identify?
- A. Device3 only
- B. Device1, Device2, and Device3
- C. Device1 only
- D. Device2 and Device3 only
- E. Device2 only
Answer: D
NEW QUESTION # 303
Your company uses Microsoft Defender for Endpoint. Microsoft Defender for Endpoint contains the device groups shown in the following table.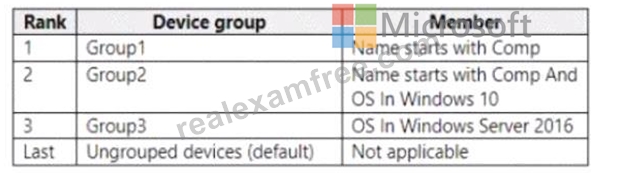
You onboard computers to Microsoft Defender for Endpoint as shown in the following table.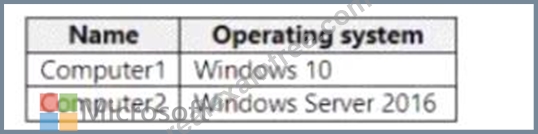
Of which groups are Computer! and Computed members? To answer, select the appropriate options in The answer area.
NOTE: Each correct selection is worth one point.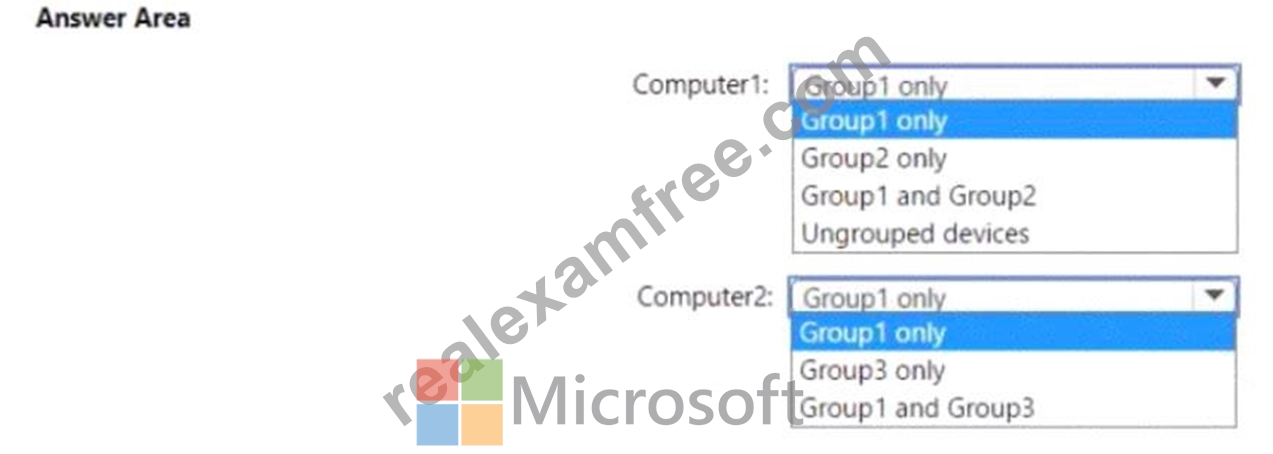
Answer:
Explanation: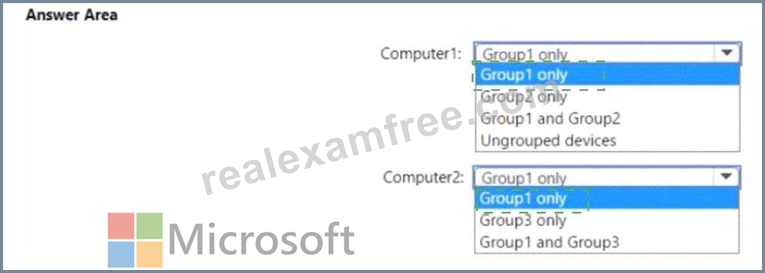
Explanation: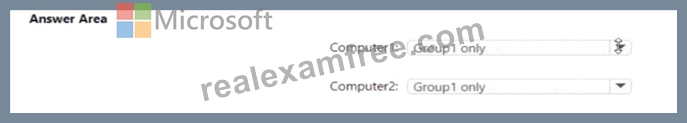
NEW QUESTION # 304
Your company uses Microsoft Defender for Endpoint. Microsoft Defender for Endpoint contains the device groups shown in the following table.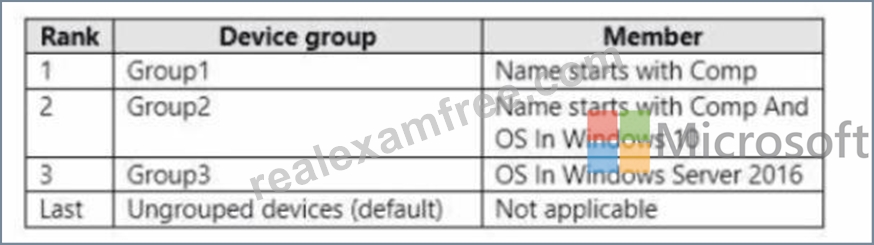
You onboard computers to Microsoft Defender for Endpoint as shown in the following table.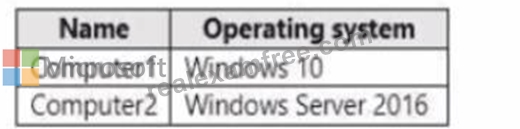
Of which groups are Computer! and Computed members? To answer, select the appropriate options in The answer area.
NOTE: Each correct selection is worth one point.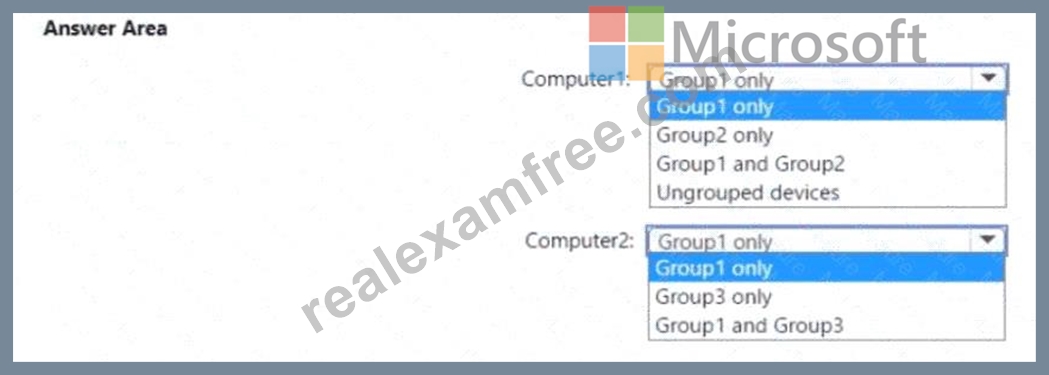
Answer:
Explanation: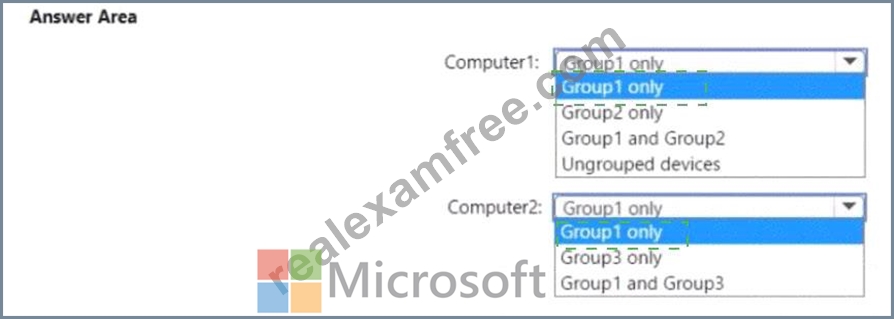
Explanation: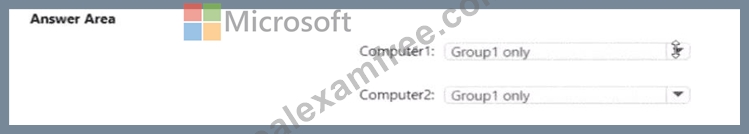
NEW QUESTION # 305
From the Security & Compliance admin center, you create a content export as shown in the exhibit. (Click the Exhibit tab.)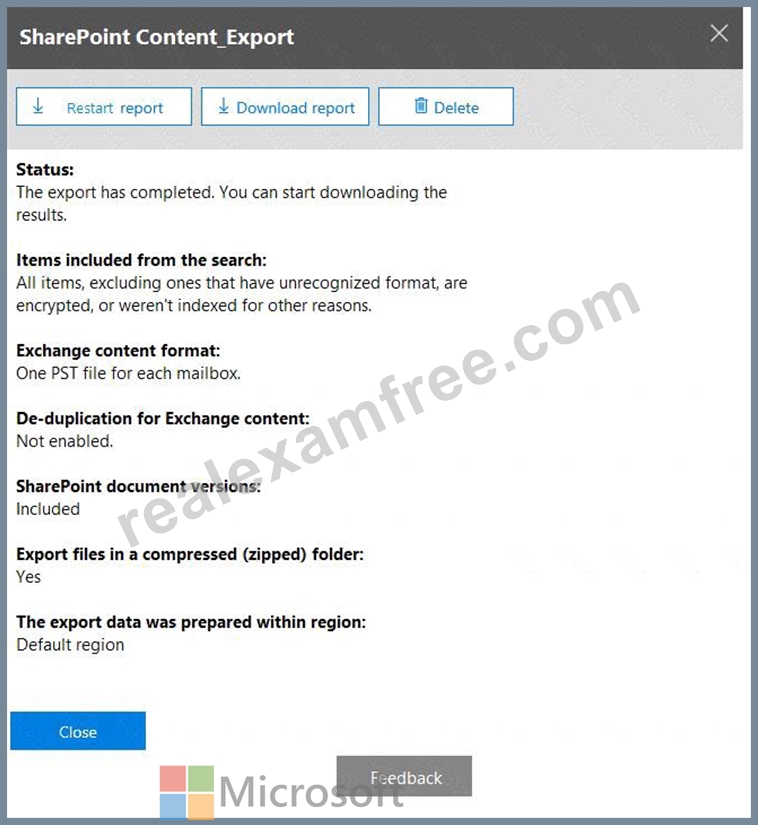
What will be excluded from the export?
- A. a 5-KB RTF file
- B. a 10-MB XLSX file
- C. an 80-MB PPTX file
- D. a 5-MB MP3 file
Answer: D
Explanation:
Unrecognized file formats are excluded from the search.
Certain types of files, such as Bitmap or MP3 files, don't contain content that can be indexed. As a result, the search indexing servers in Exchange and SharePoint don't perform full-text indexing on these types of files.
These types of files are considered to be unsupported file types.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/partially-indexed-items-in-content-search?view=o36
https://docs.microsoft.com/en-us/office365/securitycompliance/export-a-content-search-report
NEW QUESTION # 306
You have a Microsoft 365 ES subscription that has three auto retention policies as show in the following exhibit.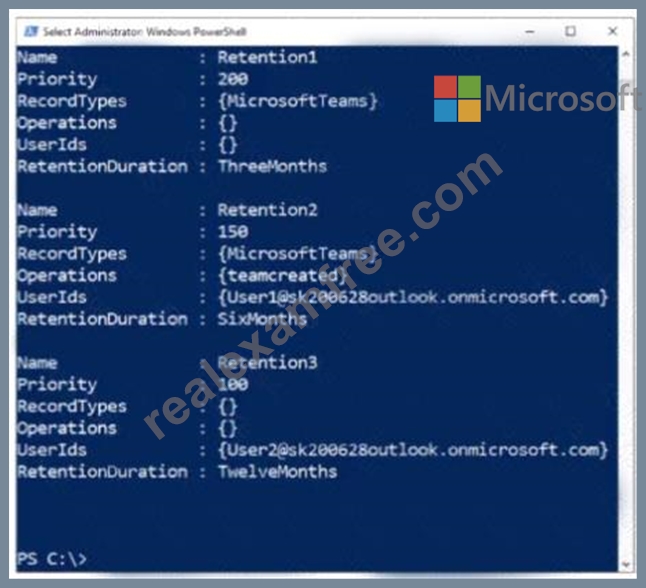
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic NOTE Each correct selection is worth one point.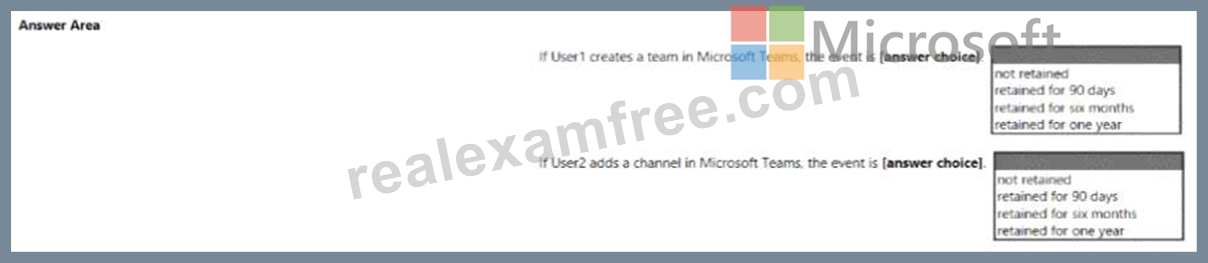
Answer:
Explanation: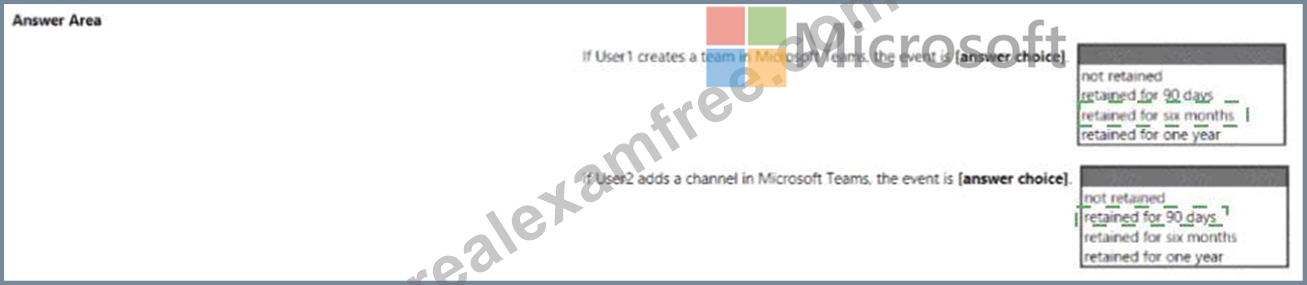
Explanation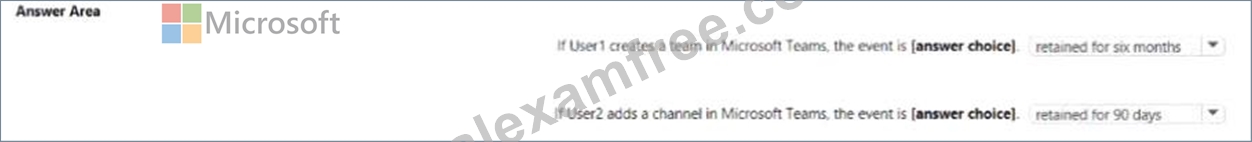
NEW QUESTION # 307
You have a Microsoft Azure Active Directory (Azure AD) tenant named Contoso.com.
You create a Microsoft Defender for identity instance Contoso.
The tenant contains the users shown in the following table.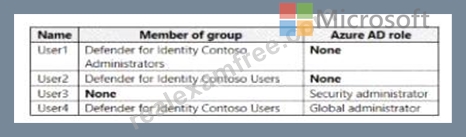
You need to modify the configuration of the Defender for identify sensors.
Solutions: You instruct User4 to modify the Defender for identity sensor configuration.
Does this meet the goal?
- A. No
- B. Yes
Answer: B
NEW QUESTION # 308
HOTSPOT
Your network contains an on-premises Active Directory forest named contoso.com. The forest contains the following domains:
* Contoso.com
* East.contoso.com
The forest contains the users shown in the following table.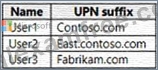
The forest syncs to an Azure AD tenant named contoso.com as shown in the exhibit. (Click the Exhibit tab.)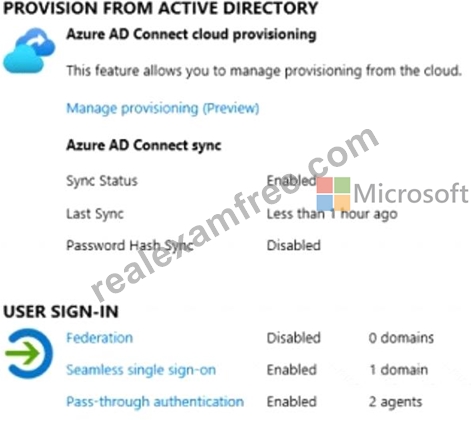
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.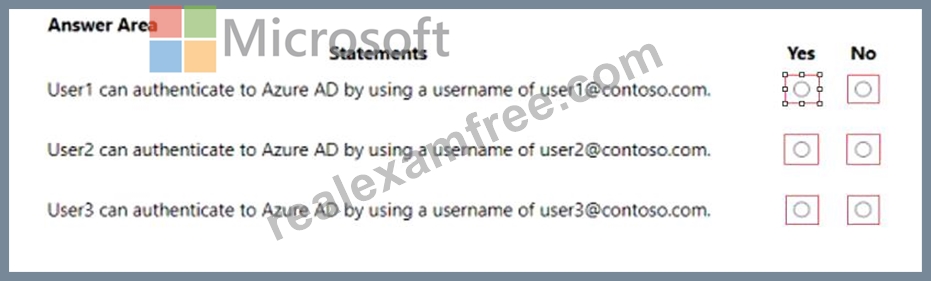
Answer:
Explanation: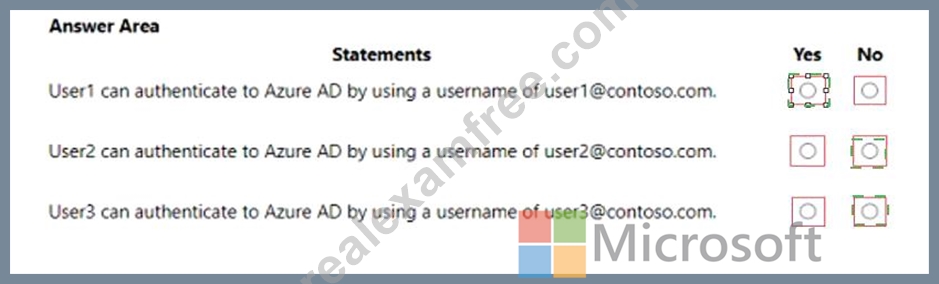
Explanation:
Box 1: Yes
The UPN of user1 is [email protected] so he can authenticate to Azure AD by using the username [email protected].
Box 2: No
The UPN of user2 is [email protected] so he cannot authenticate to Azure AD by using the username [email protected].
Box 3: No
The UPN of user3 is [email protected] so he cannot authenticate to Azure AD by using the username [email protected].
NEW QUESTION # 309
Your on-premises network contains an Active Directory domain and a Microsoft Endpoint Configuration Manager site.
You have a Microsoft 365 E5 subscription that uses Microsoft Intune.
You use Azure AD Connect to sync user objects and group objects to Azure Directory (Azure AD) Password hash synchronization is disabled.
You plan to implement co-management.
You need to configure Azure AD Connect and the domain to support co-management.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.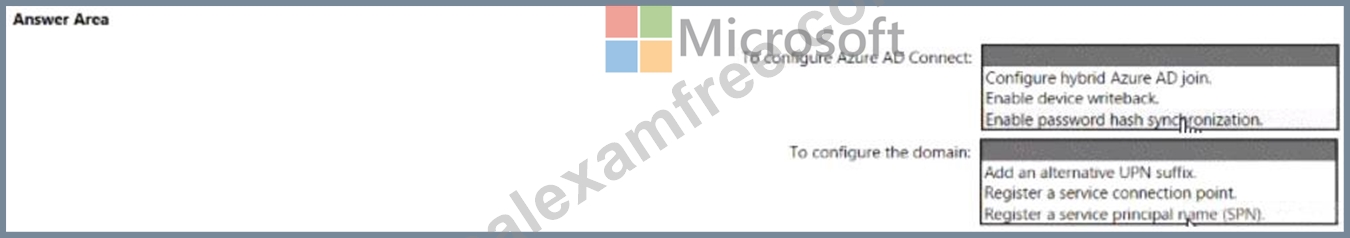
Answer:
Explanation: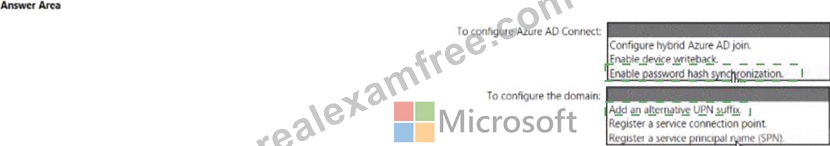
Explanation: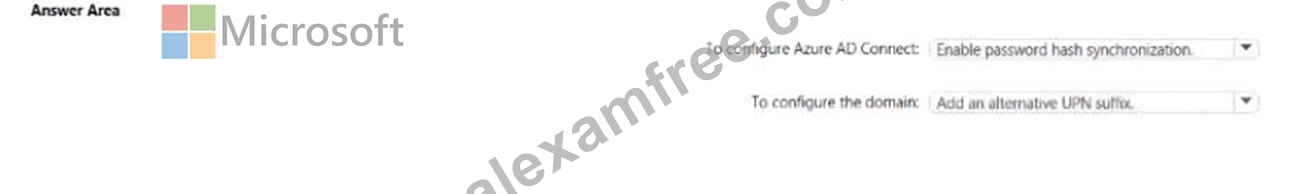
NEW QUESTION # 310
Your company purchases a cloud app named App1.
You need to ensure that you can use Microsoft Cloud App Security to block downloads in App1. App1 supports session controls.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.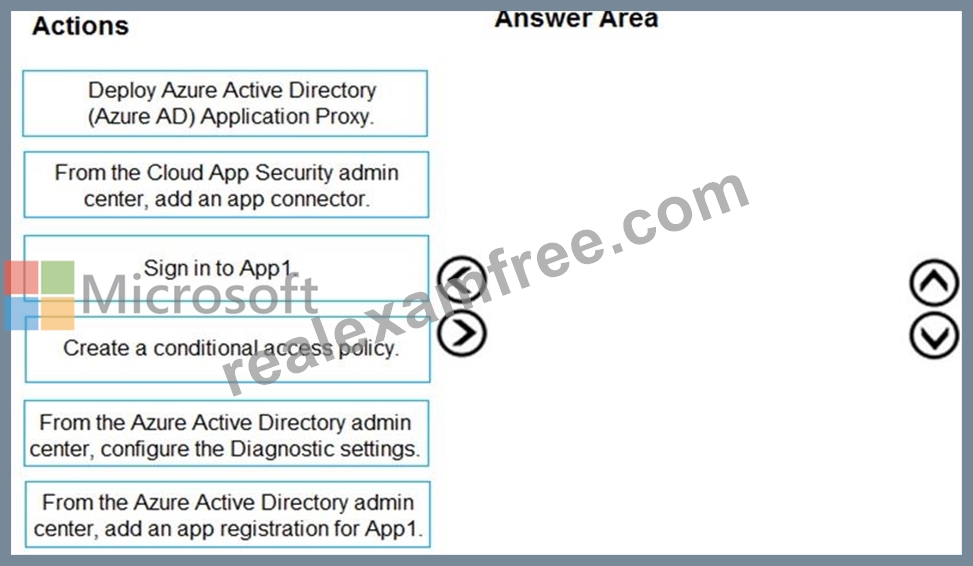
Answer:
Explanation: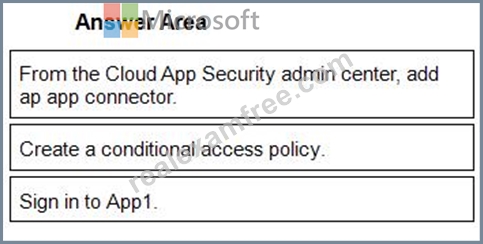
1 - From the Cloud App Security admin center, add ap app connector.
2 - Create a conditional access policy.
3 - Sign in to App1.
Reference:
https://docs.microsoft.com/en-us/cloud-app-security/getting-started-with-cloud-app-security
NEW QUESTION # 311
You have a Microsoft 365 tenant that contains devices enrolled in Microsoft Intune. The devices are configured as shown in the following table.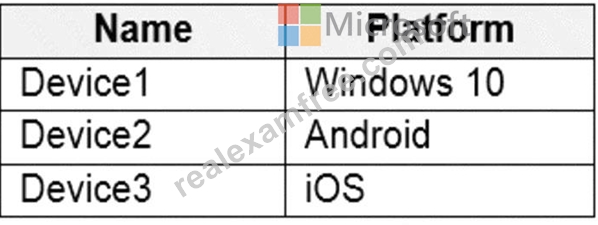
You plan to perform the following device management tasks in Microsoft Endpoint Manager:
Deploy a VPN connection by using a VPN device configuration profile.
Configure security settings by using an Endpoint Protection device configuration profile.
You support the management tasks.
What should you identify? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.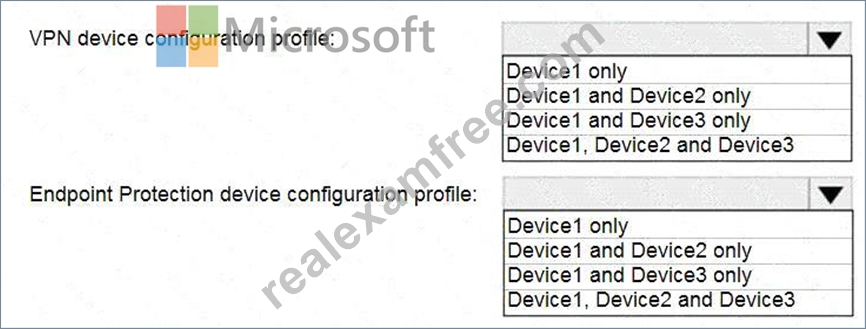
Answer:
Explanation: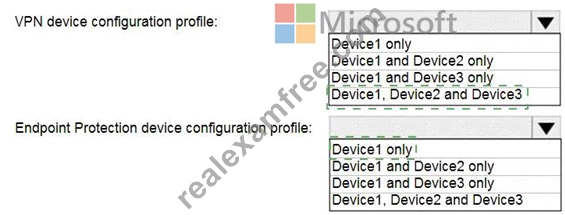
Explanation: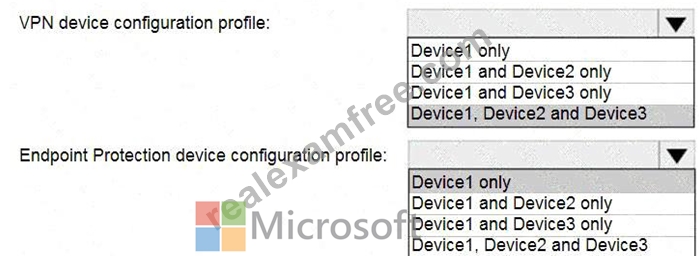
Reference:
https://docs.microsoft.com/en-us/mem/intune/configuration/vpn-settings-configure
https://docs.microsoft.com/en-us/mem/intune/protect/endpoint-protection-macos
NEW QUESTION # 312
You have a Microsoft 365 subscription that contains a Microsoft SharePoint Online site named Site1. Site1 has he files in the following table.
The Site1 users are assigned the roles shown in the following table.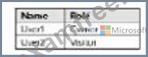
You create a data less prevention (DLP) policy names Policy1 as shown in the following exhibit.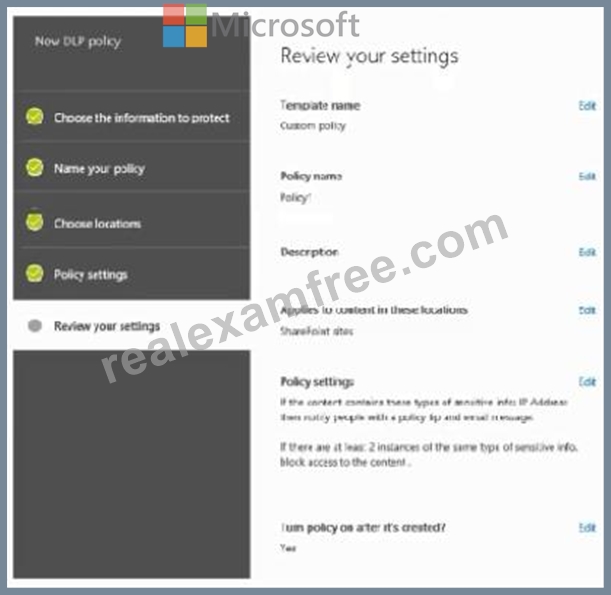
How many files will be visible to user1 and User2 after Policy' is applied to answer, selected select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: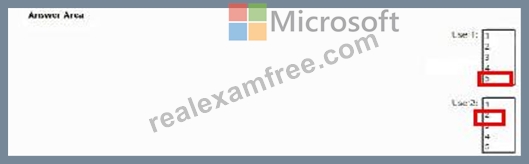
NEW QUESTION # 313
DRAG DROP
You have a Microsoft 365 E5 subscription that contains two groups named Group1 and Group2.
You need to ensure that each group can perform the tasks shown in the following table.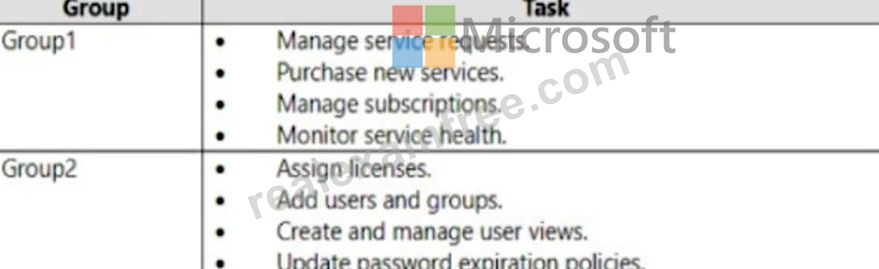
The solution must use the principle of least privilege.
Which role should you assign to each group? To answer, drag the appropriate roles to the correct groups. Each role may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.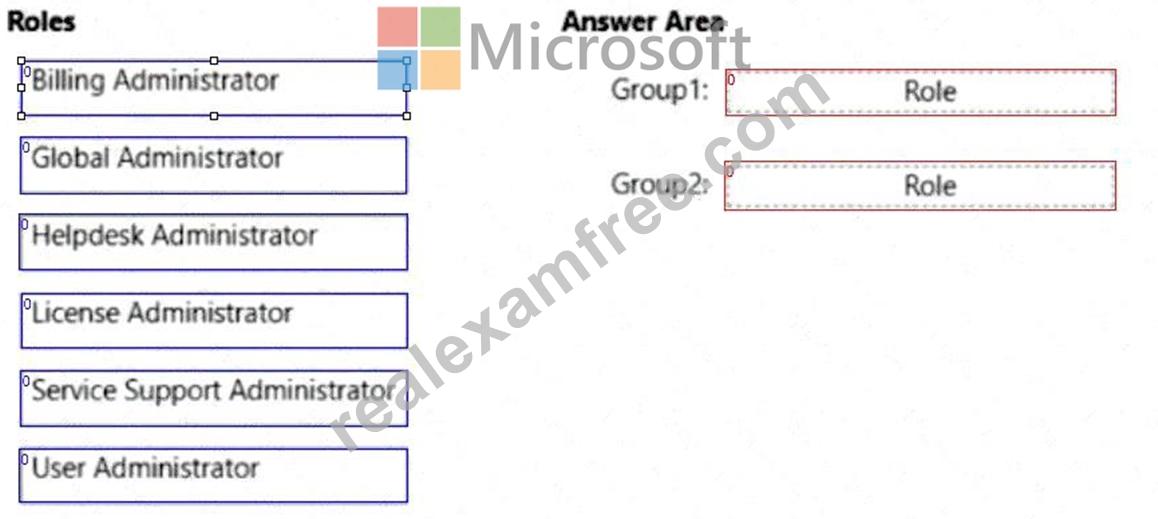
Answer:
Explanation: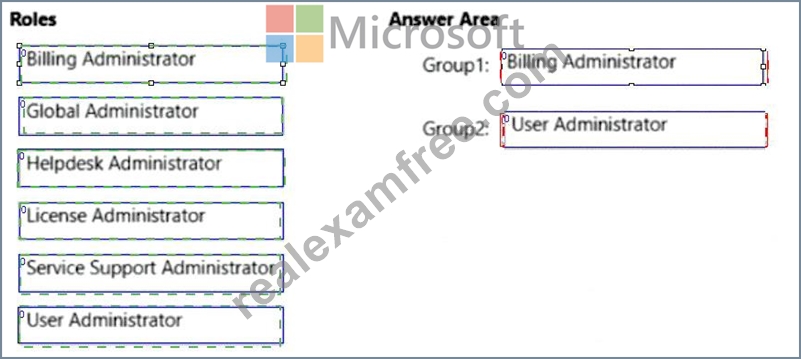
Explanation: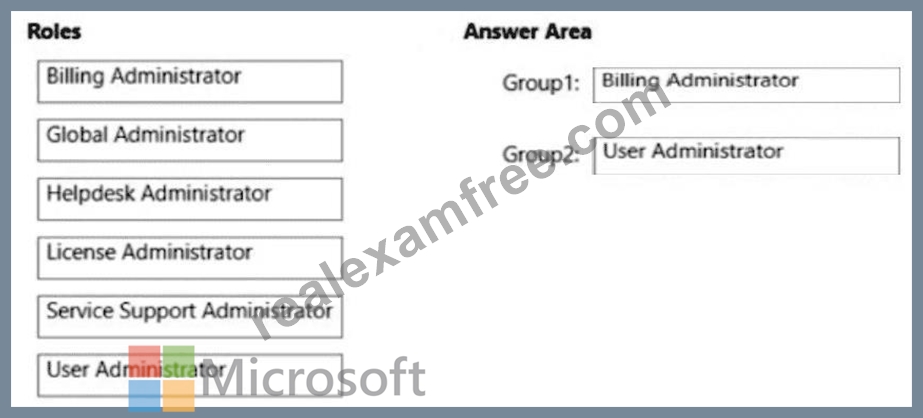
Box 1: Billing admin
manage service request
Purchase new services
Etc.
Assign the Billing admin role to users who make purchases, manage subscriptions and service requests, and monitor service health.
Box 2: User admin
User admin
Assign the User admin role to users who need to do the following for all users:
- Add users and groups
- Assign licenses
- Manage most users properties
- Create and manage user views
- Update password expiration policies
- Manage service requests
- Monitor service health
Reference:
https://learn.microsoft.com/en-us/microsoft-365/admin/add-users/about-admin-roles
NEW QUESTION # 314
You have a Microsoft 365 subscription.
You have the devices shown in the following table.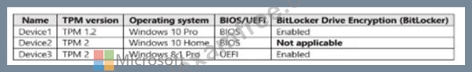
You plan to join the devices to Azure Active Directory (Azure AD)
What should you do on each device to support Azure AU join? To answer, drag the appropriate actions to the collect devices, Each action may be used once, more than once, of not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.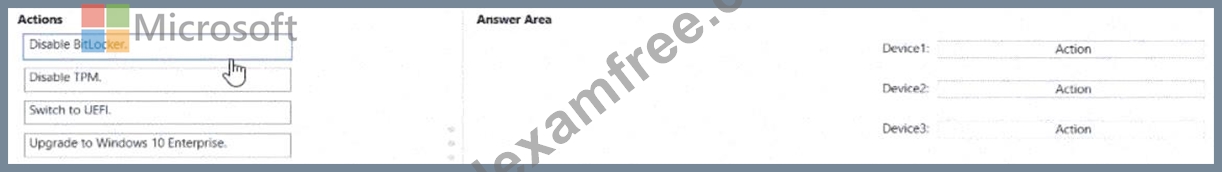
Answer:
Explanation: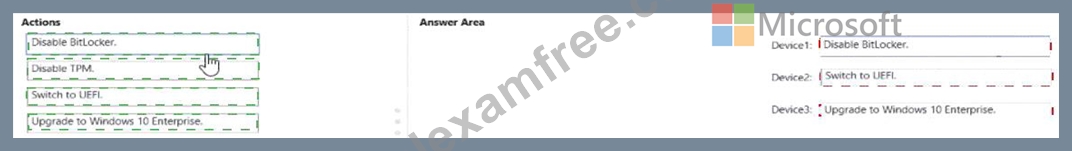
Explanation:
NEW QUESTION # 315
You have a Microsoft 365 E5 tenant that has sensitivity label support enabled for Microsoft and SharePoint Online.
You need to enable unified labeling for Microsoft 365 groups.
Which cmdlet should you run?
- A. set-unifiedGroup
- B. Add-UnifiedGroupLinks
- C. Set-Labelpolicy
- D. Execute-AzureAdLebelSync
Answer: D
NEW QUESTION # 316
You have a Microsoft 365 tenant that contains 100 Windows 10 devices. The devices are managed by using Microsoft Endpoint Manager.
You plan to create two attack surface reduction (ASR) policies named ASR1 and ASR2. ASR1 will be used to configure Microsoft Defender Application Guard. ASR2 will be used to configure Microsoft Defender SmartScreen.
Which ASR profile type should you use for each policy? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.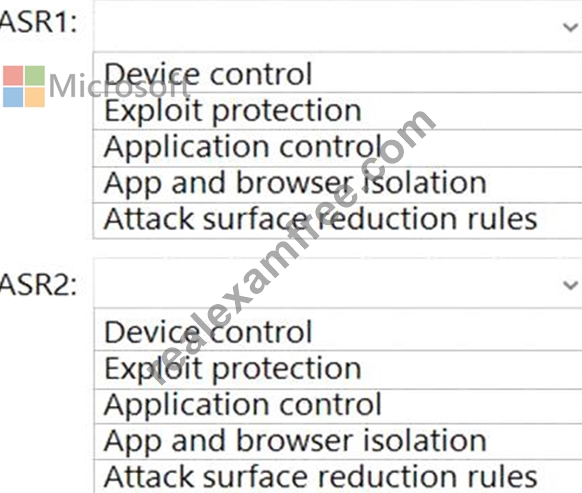
Answer:
Explanation: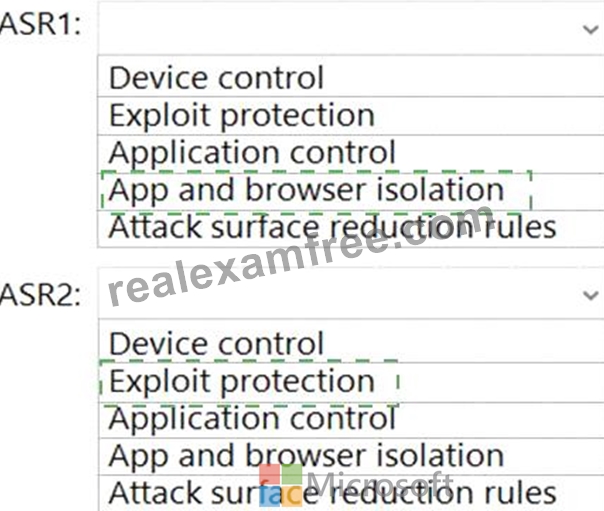
Explanation
Graphical user interface, text, application, chat or text message Description automatically generated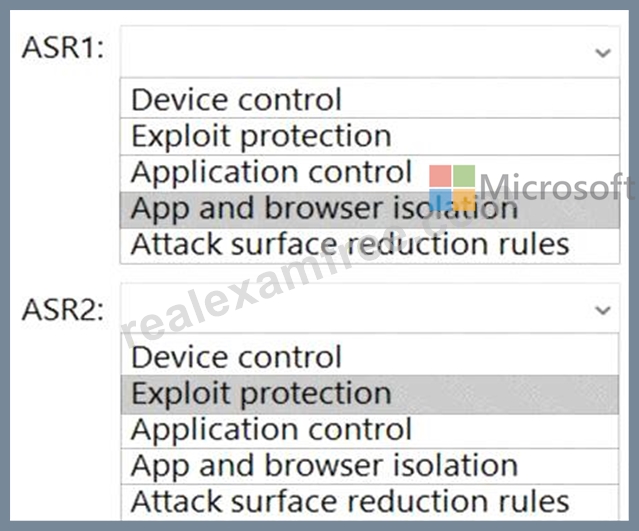
Reference:
https://docs.microsoft.com/en-us/mem/intune/protect/endpoint-security-asr-policy
NEW QUESTION # 317
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your network contains an on-premises Active Directory domain named contoso.com. The domain contains the users shown in the following table.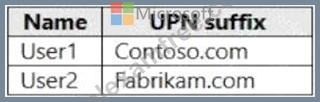
The domain syncs to an Azure AD tenant named contoso.com as shown in the exhibit. (Click the Exhibit tab.)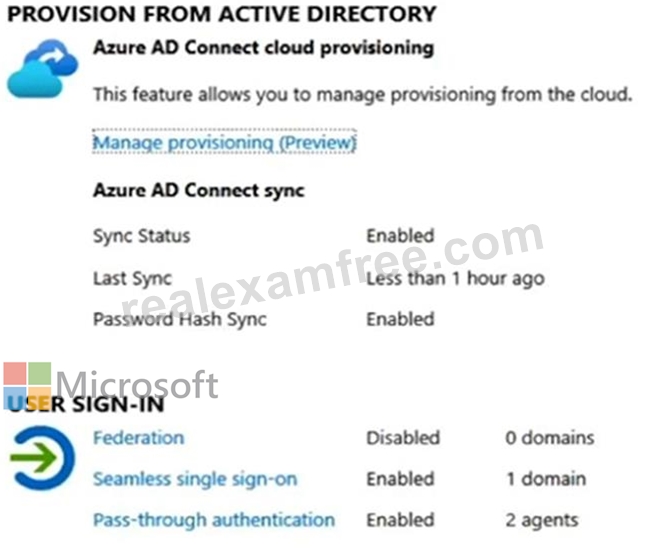
User2 fails to authenticate to Azure AD when signing in as [email protected].
You need to ensure that User2 can access the resources in Azure AD.
Solution: From the on-premises Active Directory domain, you set the UPN suffix for User2 to @contoso.com.
You instruct User2 to sign in as [email protected].
Does this meet the goal?
- A. No
- B. Yes
Answer: B
Explanation:
The on-premises Active Directory domain is named contoso.com. You can enable users to sign on using a different UPN (different domain), by adding the domain to Microsoft 365 as a custom domain. Alternatively, you can configure the user account to use the existing domain (contoso.com).
NEW QUESTION # 318
You have a Microsoft 365 E5 subscription that uses Microsoft Defender for Endpoint.
When users attempt to access the portal of a partner company, they receive the message shown in the following exhibit.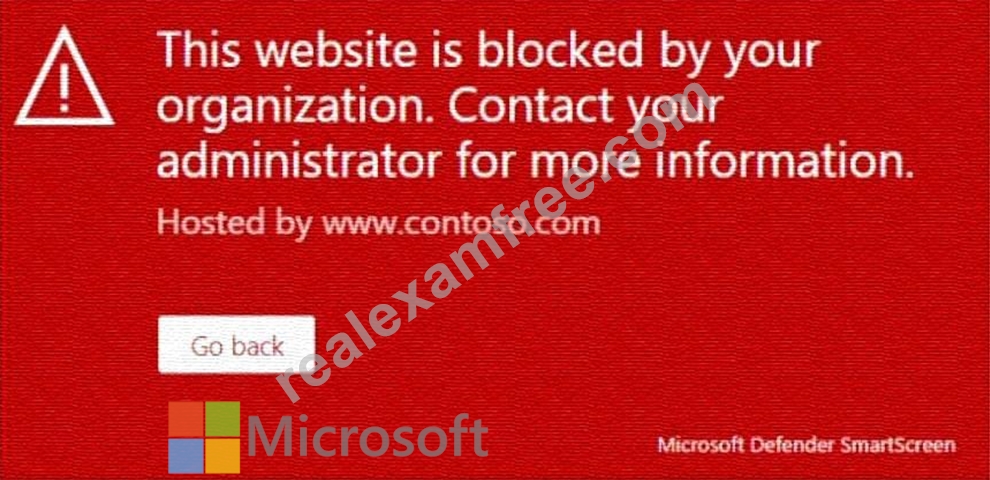
You need to enable user access to the partner company's portal.
Which Microsoft Defender for Endpoint setting should you modify?
- A. Alert notifications
- B. Custom detections
- C. Indicators
- D. Advanced hunting
- E. Alert suppression
Answer: C
Explanation: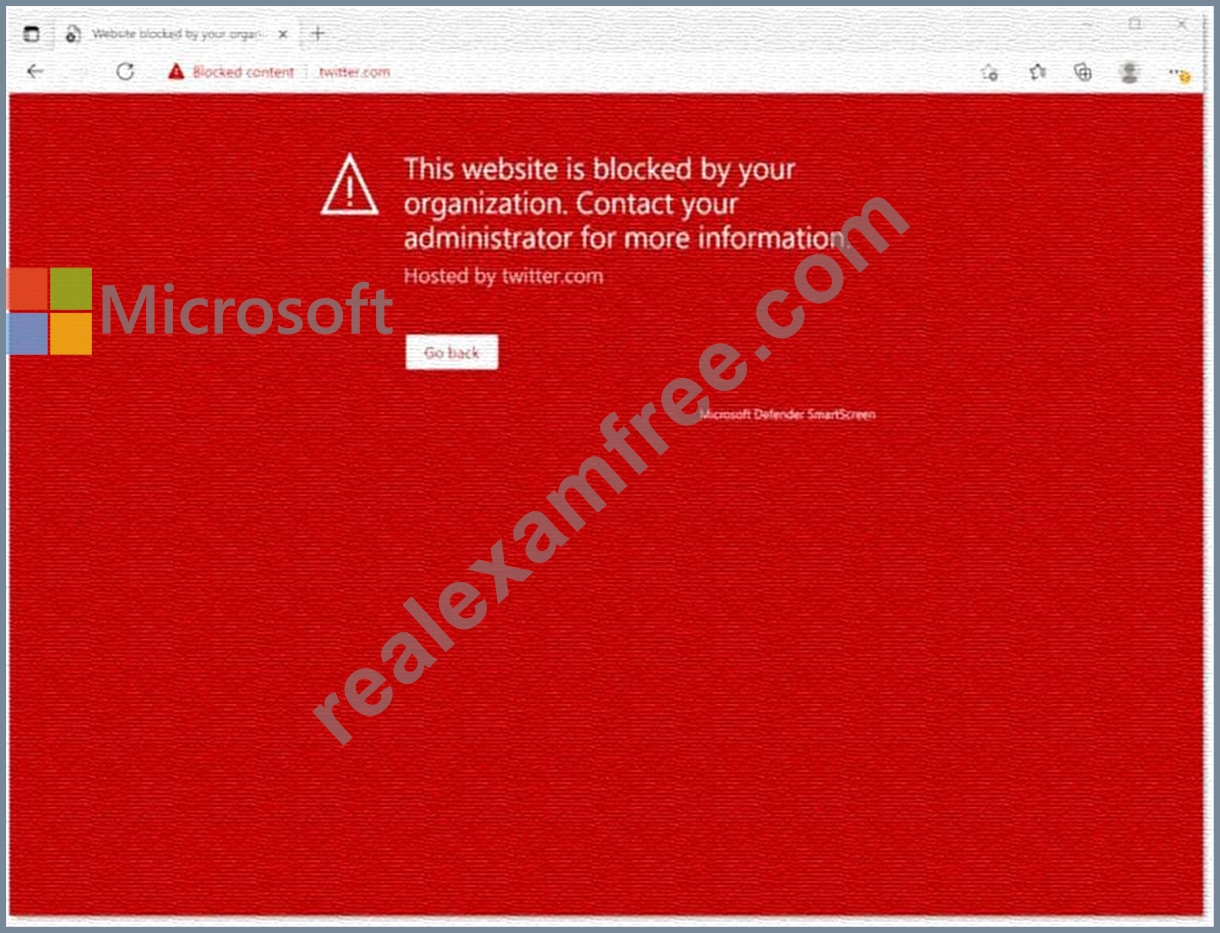
This Website Is Blocked By Your Organization
Custom indicators will block malicious IPs, URLs, and domains. Then, they will display the above message for the user.
Reference:
https://jadexstrategic.com/web-protection/
NEW QUESTION # 319
You have a Microsoft 365 E5 subscription that includes the following active eDiscovery case:
* Name: Case1
* Included content: Group1, User1, Site1
* Hold location: Exchange mailboxes, SharePoint sites, Exchange public folders The investigation for Case1 completes, and you close the case.
What occurs after you close Case1? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.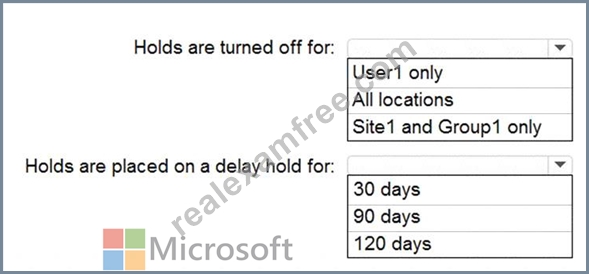
Answer:
Explanation: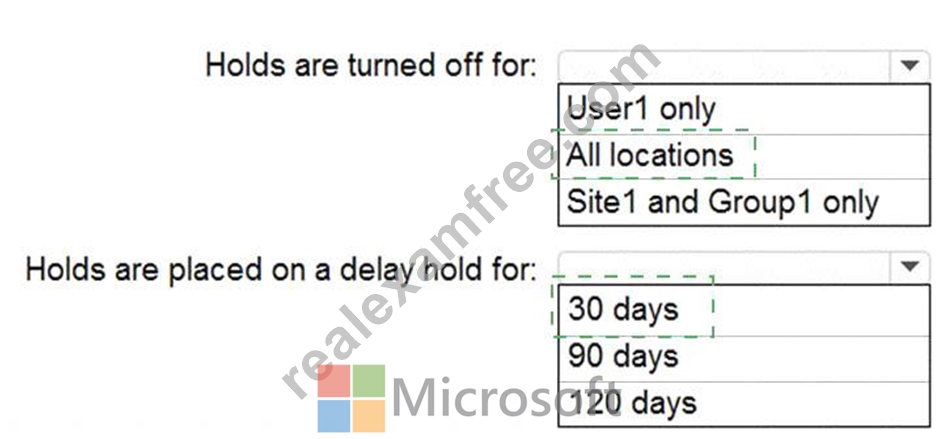
Explanation
Graphical user interface, text, application Description automatically generated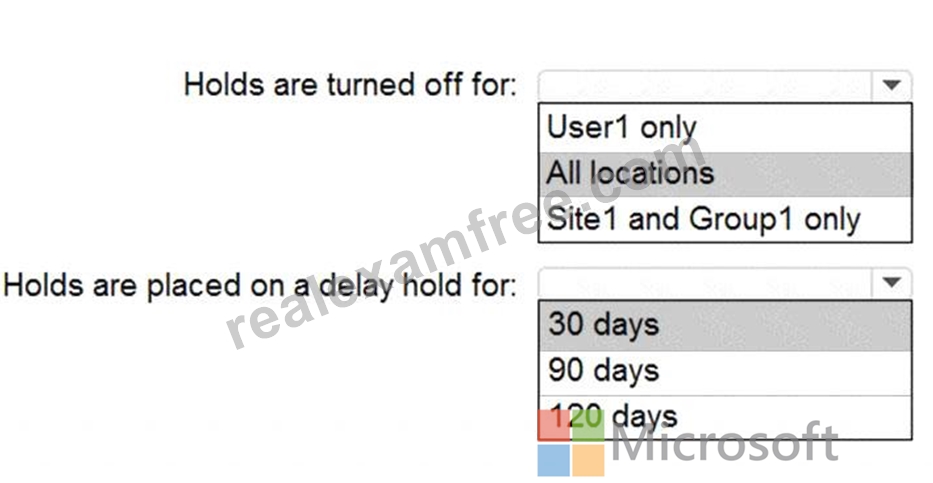
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/close-or-delete-case?view=o365-worldwide
NEW QUESTION # 320
You have an Azure AD tenant that contains the users shown in the following table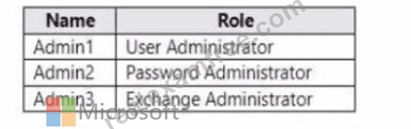
You need to compare the permissions of each role. The solution must minimize administrative effort.
Which portal should you use?
- A. the Microsoft 365 admin center
- B. the Microsoft Purview compliance portal
- C. the Microsoft 365 Defender portt1
- D. the Microsoft Entra admin center
Answer: B
NEW QUESTION # 321
......
Microsoft MS-102 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
MS-102 Actual Questions and Braindumps: https://passleader.realexamfree.com/MS-102-real-exam-dumps.html
